Agentic Security Testing for Web Apps and APIs
Supervisor-led AI agents map your web app and APIs, test OWASP Top 10, API and business-logic flaws, confirm each issue live, and hand tester-reviewed findings with evidence to your team.
- Capability:
- AI Security & Compliance
- Industry:
- SaaS & AI Product Companies
Who it is for
- CTO or VP Engineering
- Head of Security
- AppSec Lead
- Penetration Testing Service Provider
The problem
SaaS teams ship web and API changes every week, but a full manual pentest happens once or twice a year. Scanners run more often but produce long lists of unverified issues and miss business-logic flaws, such as a user approving their own expense claim or reading another account's invoice by changing an ID.
Pentests that age quickly
Last year's report says little about the endpoints and roles added since.
Scanner noise
Unverified scanner output buries real issues and costs engineers time on false positives.
Business logic missed
Authorisation and workflow flaws need an understanding of roles and intent that signature-based scanners lack.
Weak evidence
Findings without a reproducible path are hard for developers to fix and hard for customers to trust.
What we build
We build and run an agentic testing workflow for your web application and APIs. A supervisor agent plans the engagement and directs specialist agents: one discovers endpoints from crawling, OpenAPI or GraphQL schemas and traffic captures; another maps roles and the attack surface; others test for OWASP Top 10 and OWASP API Security Top 10 risks, such as broken object-level authorisation, and work through business-logic flows. Every candidate issue is confirmed live in a controlled way, so only real issues are reported, with the requests and responses that prove them. A human tester reviews findings, looks for chains across issues and rates severity. Findings can become draft fix pull requests for developer review.
- Endpoint discovery from crawling, OpenAPI or GraphQL schemas and traffic captures
- Role and permission matrix testing across user types and tenants
- OWASP Top 10 and OWASP API Security Top 10 coverage
- Business-logic testing of workflows such as approvals, refunds and invitations
- Live confirmation of each candidate issue with request and response evidence
- Tester-reviewed findings, with optional draft fix pull requests
How it works
- 01Agree scope and accountsWe agree targets, environments, test accounts per role, rate limits and excluded actions.
- 02Discover and mapAgents discover endpoints and build a map of roles, objects and workflows.
- 03Plan and testThe supervisor assigns specialist agents to test each area against OWASP and business-logic cases.
- 04Confirm liveEach candidate issue is reproduced safely, and unconfirmed issues are dropped.
- 05Tester reviewA human tester reviews confirmed issues, looks for chains and rates severity.
- 06Report and fixFindings go to your tracker with evidence, and draft fix pull requests are prepared where useful.

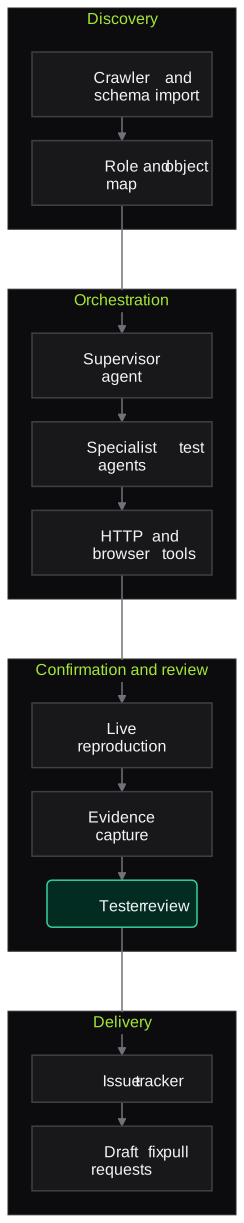
Architecture
- Discovery
- Crawler and schema importer
- Traffic capture import
- Role and object map
- Orchestration
- Supervisor agent with test plan
- Specialist agents for authentication, access control, injection and logic
- Tool layer for HTTP requests and browser automation
- Confirmation
- Live reproduction under a safe-testing policy
- Evidence capture of requests and responses
- Review
- Tester console
- Severity and chain analysis
- Delivery
- Issue tracker integration
- Draft fix pull requests
- Retest scheduler
Inputs and outputs
Inputs
- Target URLs and API base paths in staging
- OpenAPI or GraphQL schemas, where available
- Test accounts for each role and tenant
- Description of key business workflows
- Exclusions and rate limits
Outputs
- Endpoint and role map
- Confirmed findings with request and response evidence
- Severity ratings and chain analysis
- Tickets in your issue tracker
- Draft fix pull requests for developer review
Where people stay in control
A human tester reviews every confirmed finding, looks for chains and sets severity. Developers review and merge any draft fix pull request; nothing changes in your code without their approval.
Integrations
- Staging environment and test accounts
- OpenAPI or GraphQL schemas
- Issue trackers such as Jira, Linear or GitHub Issues
- Source repository for draft fix pull requests
- CI for scheduled retests
Guardrails
- Agreed scope, exclusions and rate limits enforced by the tool layer
- No destructive actions; state-changing tests only on test accounts
- Every reported issue confirmed live before it is reported
- All agent actions logged for audit
- Stop control available to your team throughout
Compliance notes
- Testing records support customer due diligence and audits against frameworks such as ISO/IEC 27001 and SOC 2, where regular pentesting is expected.
- Findings map to the OWASP Top 10 and OWASP API Security Top 10.
A typical pilot
Duration: 3 weeks
One web application and its main API in staging, with test accounts for two or three roles.
Deliverables
- 01Endpoint and role map
- 02Confirmed findings with evidence
- 03Tester-reviewed report
- 04Draft fix pull requests for selected findings
- 05Retest results
What we measure
- Confirmed findings by severity
- Count of confirmed issues after tester review.
- Candidates rejected at review
- Candidates the tester rejects as not real, tracked to tune the agents.
- Endpoint coverage
- Endpoints discovered and tested against known endpoints from schemas.
- Fix turnaround
- Time from ticket to passing retest, including draft pull requests.
Built on related work
Agentic AI penetration-testing platform
NZ penetration-testing-as-a-service company (anonymised)
Supervisor-based multi-agent platform for endpoint discovery, attack-surface mapping, OWASP Top 10 and business-logic testing, live vulnerability validation and exploit-chain evidence.
FAQs
01Is this a replacement for a manual pentest?
It takes over much of the repetitive work and can run far more often, but a human tester still reviews findings, looks for chains and judges severity. Many teams use it between annual manual tests or as the base of a continuous programme.
02Is it safe to run against our app?
Testing runs in staging with test accounts, within agreed rate limits and exclusions. Agents avoid destructive actions, and your team can stop a run at any time.
03Can it test business logic?
Yes, within the workflows you describe and the roles we have accounts for. Logic testing works best when your team walks us through how approvals, refunds or sharing should behave.
04Do you fix the issues?
We can prepare draft fix pull requests for confirmed findings. Your developers review, test and merge them, and we retest afterwards.
Related use cases
- SaaS & AI Product Companies
LLM Application Penetration Test (OWASP LLM Top 10)
A scoped pentest of your LLM feature and the app around it: prompt injection, data disclosure, output handling, excessive agency and system-prompt leakage, with reproducible evidence.
- SaaS & AI Product Companies
AI Agent Red-Teaming (Tool Misuse and Goal Hijack)
Red-team your AI agents for goal hijacking, tool misuse, excessive agency, privilege abuse and memory poisoning, in a sandbox that records every tool call and decision.
- SaaS & AI Product Companies
Continuous AI Security Regression in CI
Run versioned prompt-injection, jailbreak and data-leakage suites in CI on every prompt, model, tool or index change, and block releases that regress past agreed severity thresholds.
- Fintech & Payments
Pre-Launch Security Assessment for LLM Features
Test a new chatbot, copilot or LLM feature for prompt injection, cross-customer data leakage, off-policy answers and unsafe output handling before release, with evidence and a retest.

Founded by Akhilesh Mittal. 8 years building a security platform for a New Zealand company. IIT ISM Dhanbad and IMT Ghaziabad. Builds production agentic AI.
Scope a first test on one AI feature
Pick the LLM feature, agent or voice bot that worries you most. We will agree a short written scope and show you verified findings with evidence.